What Nadella argued
On October 10, 2026, Satya Nadella published an argument titled "Models as Insider Risks in the Super Intelligence Era" on his X account. In it he contends that enterprise AI should be treated like an insider risk: a capable actor with access to your systems whose behavior you cannot fully predict or trust by default.
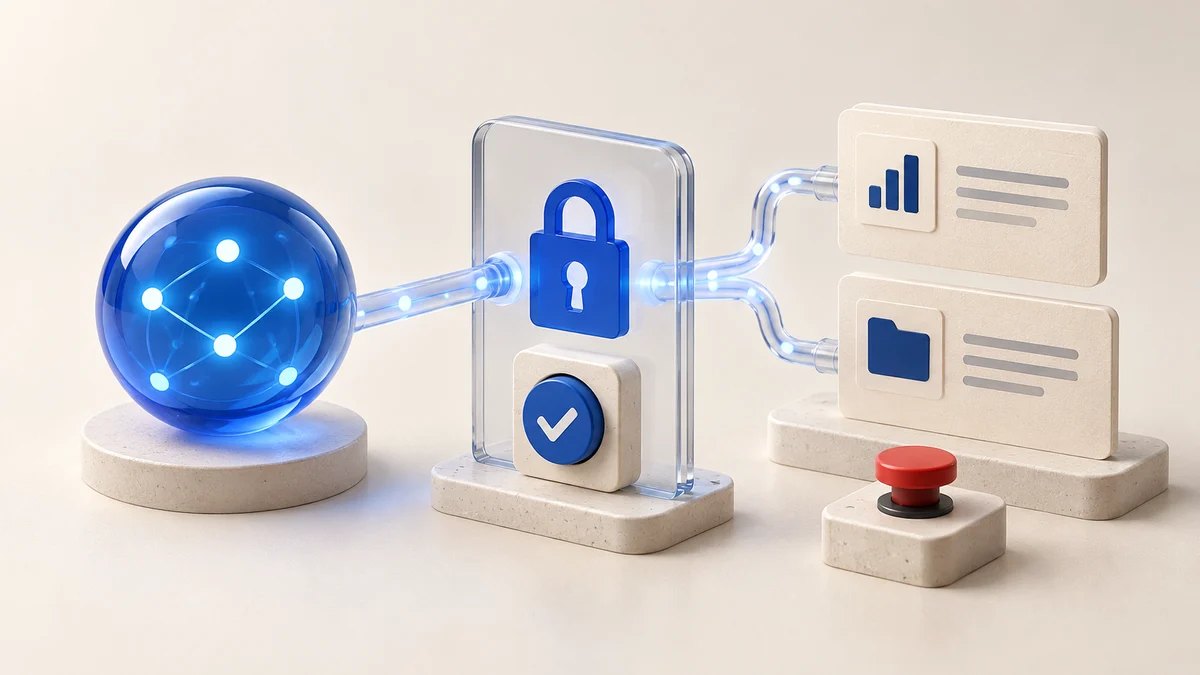
His central recommendation is that controls must live outside the model itself. He calls for observable actions, independent access controls and auditability, testing, containment, and the ability of an authorized person to pause or stop a model in the middle of a task. These are his stated recommendations, not findings from a benchmark or a shipped feature.
It is important to separate this from what it is not. Nadella did not announce that Microsoft released an emergency-brake product, and no industry standard was established by these sources. The statement is a governance viewpoint from the CEO of a major vendor, which gives it weight but does not make its claims proven.
How independent outlets reported it
CNBC independently attributed the argument to Nadella on October 10, describing his call for safeguards and a human-controlled emergency brake. The Verge published its own report the same day, characterizing his position as one that assumes models should be treated as potentially compromised from the start.
Both outlets describe the same underlying statement rather than a new announcement. That matters: the novelty here is the dated public statement itself, not a product launch or measured result. Readers should treat the substance of Nadella's claims as his argument to evaluate, not as established fact.
What this means for your business
If an AI workflow is connected to customer records or quoting tools, it can take actions beyond what staff intended. The practical response Nadella's framing points toward is a concrete system: a quote-preparation workflow that reads approved intake and customer records, prepares a draft, and requires staff approval before a separate application sends the quote or writes to billing.
In such a design, the application enforces role-based access and allowed actions outside the model, records inputs, outputs, and reviewer decisions, and offers a tested stop or disable control. The expected benefit is clearer accountability, fewer uncontrolled handoffs, and easier review of changes before customers receive them. Detailed In Design builds this kind of custom AI and software integration with human-reviewed workflow outputs.
The limitations are real and worth stating plainly. A pause request cannot recall an email that has already been sent or a third-party transaction that is complete. Logging may contain sensitive data, so retention should be limited to what is needed. Human approval and controls reduce exposure but do not make model output correct or eliminate compromise. No vendor partnership, ownership claim, or endorsement by Microsoft is implied.
A restrained next step
If you run AI against customer data or billing tools, the useful first move is to map where a model can act without a human gate and which actions are irreversible once taken. From there, define permissions, review capacity, and logging boundaries before scaling usage. That assessment is a project requirement, not a guarantee of tamper-proof infrastructure.
Sources and original reporting
- Satya Nadella: Models as Insider Risks in the Super Intelligence Era
- Microsoft's Satya Nadella says AI models need an emergency brake for safety
- Satya Nadella says we should assume all AI models are compromised
Share this story
Use More apps or Copy link for Instagram, Threads, YouTube, and other platforms.